
- Product
- Increase Client Engagement
- Elevating the Client Experience
- Minimize Operational Inefficiencies
Product Features
Client Outcomes
Discover the three pillars that drive everything we do.
- Services
- Increase Client Engagement
- Elevating the Client Experience
- Minimize Operational Inefficiencies
Professional Services
Client Outcomes
Discover the three pillars that drive everything we do.
- Resources
- Increase Client Engagement
- Elevating the Client Experience
- Minimize Operational Inefficiencies
Resources
Client Outcomes
Discover the three pillars that drive everything we do.


Email Tracking Pixels Now Require Consent in France and Italy.
Email tracking pixels are now treated like cookies under GDPR and the ePrivacy Directive, which means consent and documentation matter more than they used to. ConsentTrack tracks each contact exactly as far as their consent allows, without losing your campaign-level view.

Inside the CNIL and Garante Guidance
Neither the CNIL nor the Garante wrote a new law this year. Both clarified how existing GDPR and ePrivacy rules apply to email tracking pixels, treating them the same way as cookies: something that needs consent unless a narrow exemption applies. The core position is the same in both countries: consent to receive marketing emails and consent to be tracked inside them are separate permissions.
France's CNIL deadline was July 14, 2026, and has already passed, with a narrow exemption for deliverability purposes only. Italy's Garante deadline is October 28, 2026, and its exemption is narrower still, limited to aggregate, anonymized statistics. Both expect consent withdrawal to be easy, including retroactively for emails already sitting unopened.
Three Gaps Most Compliance Teams Are About to Discover
1. One Consent Record, Doing Two Jobs
Most CRMs and ESPs store a single marketing opt-in and treat it as covering tracking too. Under both rulings, that distinction now matters. If tracking consent and email consent aren't separated in your own records, that's worth a closer look.
2. No Audit Trail on Withdrawal
It's not enough to stop tracking someone going forward. The guidance points toward a documented, timestamped record of when consent was given or withdrawn, and evidence that the withdrawal actually took effect, including for messages already sent.
3. Jurisdiction Gets Decided by the Recipient, Not the Sender
The rules apply based on where the recipient is when they open the email, not where your organization is headquartered. A single send to a mixed list of UK, French, and Italian contacts may need three different tracking treatments at once, and most platforms only offer one setting per campaign.
What "Compliant" Actually Looks Like
The rulings don't ask you to abandon email measurement, just to justify it, limit it, and document it well enough to hold up under scrutiny. Exactly what this means for your organization depends on your own audience, but here's a good starting point.
- Identify your in-scope contacts. Pull a list of everyone in France and Italy, since the rules apply based on where the recipient is, not where you're sending from.
- Separate tracking consent from marketing consent. Signup forms and preference centers need to ask for these as two distinct permissions, not one checkbox covering both.
- Give people a way to opt out of tracking without unsubscribing. Both regulators expect this to be independent of the marketing subscription itself.
- Run a notice or re-permission pass on existing contacts. For anyone already on your list who hasn't been asked about tracking specifically, a one-time notice explaining the change and offering an easy opt-in closes the gap.
- Update new-contact intake. Any signup form, landing page, or CRM integration that adds French or Italian contacts going forward should capture tracking consent from day one, not as an afterthought.
How StoneShot ConsentTrack Meets This
ConsentTrack was built in 2018, well before this became a regulatory question. The architecture that solved that problem is the same one that satisfies these rulings today.
How consent is captured and recorded
Contacts can be elevated to full tracking three ways: a consent flag synced from your CRM, an opt-in through a StoneShot preference form, or a list import explicitly marked as consented. Every change is timestamped.
How it's applied per contact
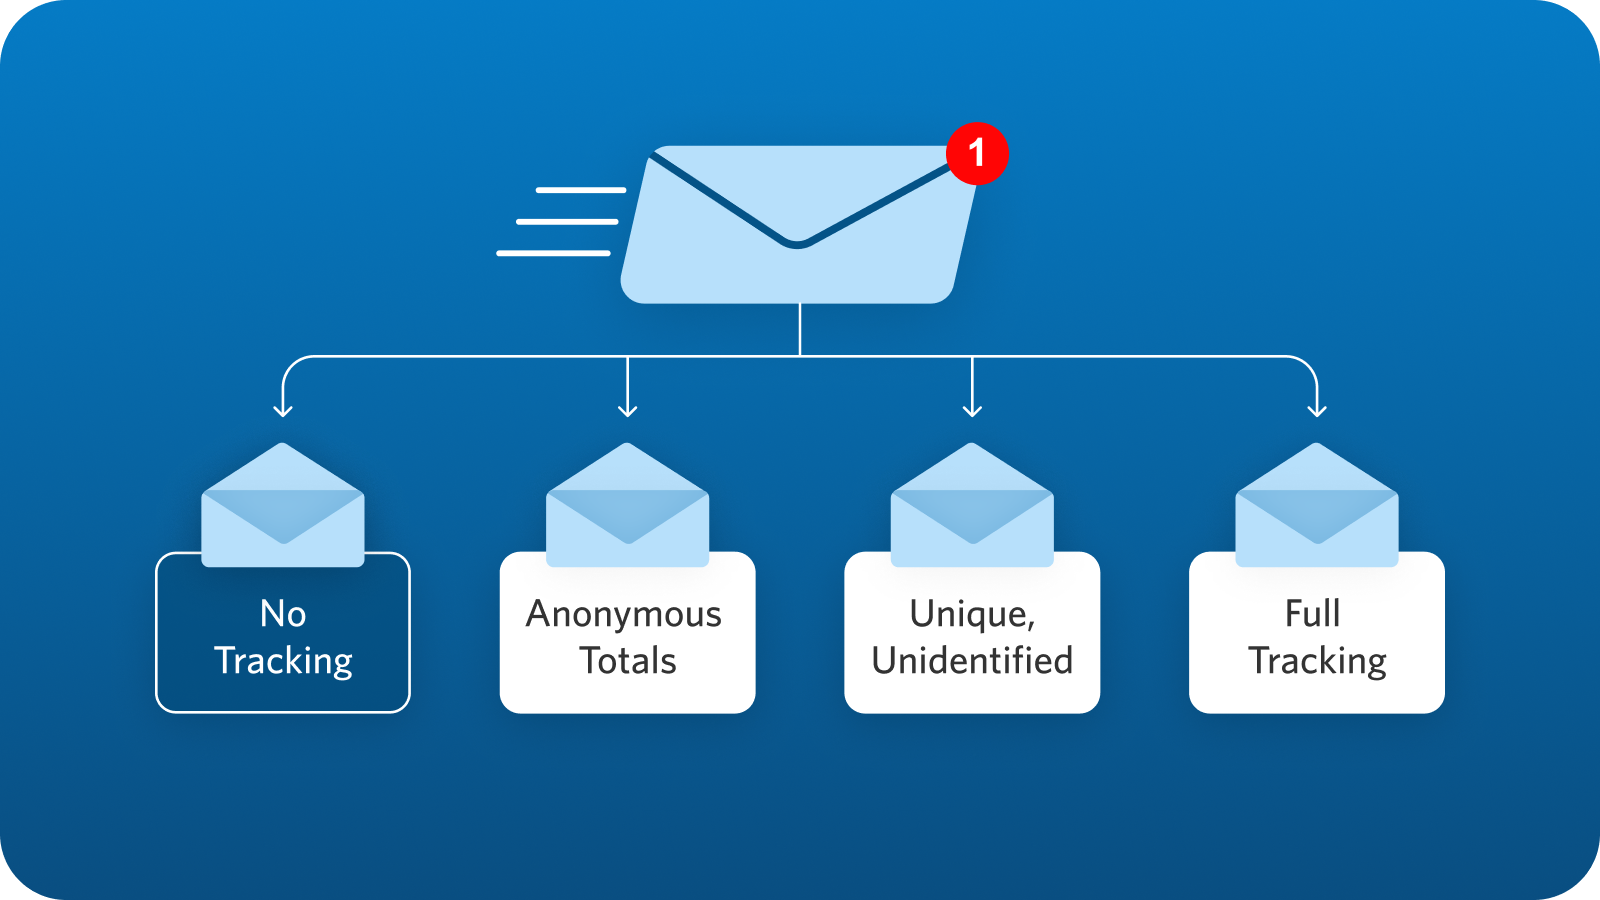
Each contact carries one of three tracking statuses:
- Optin – Consent given, full individual-level tracking applies.
- Optout – Consent declined or withdrawn, no tracking at all. Links route straight to the destination with no pixel and no redirect.
- Unverified – No consent captured yet. The contact falls back to your account's anonymized default, either Campaign Only (one shared token, aggregate totals only) or Campaign-Unique (a per-recipient token that supports accurate unique counts without identifying anyone).
How mixed jurisdictions are handled
One list, one send, each contact measured at the level their own consent status and account default allow. No separate campaigns per country, no manual list-splitting to stay compliant.
Let's Talk
Want to see how ConsentTrack works compared to your current setup? We're happy to talk it through.
Disclaimer: The regulatory information on this page, including the CNIL and Garante requirements, deadlines, and checklist above, is provided for general informational purposes and doesn't constitute legal advice. Regulations continue to evolve, and how they apply to your organization will depend on your specific setup and the jurisdictions your list touches. We'd recommend checking with legal counsel or your Data Protection Officer before making changes to your tracking or consent practices.
